Email authentication is essential for protecting your domain from spoofing, phishing, and other email-based threats.
A DMARC checker tool provides a quick and reliable way to test your DNS authentication record, identify configuration errors, and verify whether your DMARC policy is properly implemented.
By checking how DMARC works with SPF and DKIM, reviewing common record errors, and monitoring authentication reports, you can improve email security, maintain domain reputation, and support better email deliverability.
This guide explains how to use a DMARC checker tool to validate your record and keep your domain authentication properly configured.
What a DMARC Checker Is and Why DNS Authentication Matters
Implementing a robust email authentication protocol is essential to safeguarding your business domain from malicious actors. One of the most effective ways to achieve this is through the use of a DMARC checker—an online tool designed to perform rapid DMARC record lookup, validation, and analysis on a domain name.
DMARC (Domain-based Message Authentication, Reporting, and Conformance) relies heavily on proper DNS authentication because it ensures only authorized senders can dispatch emails on behalf of your organization.
When you create or modify your DMARC record (published as a TXT record under the _dmarc sub-domain, such as _dmarc.example.com), you inform ISPs like Google and Yahoo how to handle emails that fail authentication checks.
Without precise DMARC configuration and ongoing DMARC validation, your company remains vulnerable to phishing attacks and domain spoofing. A DMARC diagnostic tool assists domain owners by highlighting misconfiguration detection and verifying all critical DMARC tags and values.
The ability to perform instant DMARC record testing and DMARC record lookup is key to maintaining strong email security and compliance with sender requirements. Rapid identification of issues via a DMARC record checker enables agile troubleshooting, strengthens overall email deliverability, and supports regulatory needs.
How DMARC Works with SPF and DKIM to Protect Your Domain
DMARC builds on two core authentication protocols: SPF (Sender Policy Framework) and DKIM (DomainKeys Identified Mail). DMARC’s unique advantage is that it enforces domain-level alignment across these mechanisms, dramatically improving phishing protection and spoofing protection.
SPF and DKIM: The Building Blocks
SPF Alignment: Establishes which mail servers are authorized to send emails for your domain name and checks whether the sending server’s IP matches the list in your SPF record.
DKIM Alignment: Uses cryptographic signatures (placed in the email’s header) to validate the integrity and authenticity of outgoing messages. The public key is published as a DNS record under your domain to allow verification by recipients.
DMARC requires both SPF and DKIM to pass (or at least one, based on your policy), and more importantly, the “header-From” domain must align (match) with the authenticated domains—a process referred to as alignment mode, controlled by the adkim tag (DKIM alignment) and aspf tag (SPF alignment).
The Power of DMARC Enforced Policies
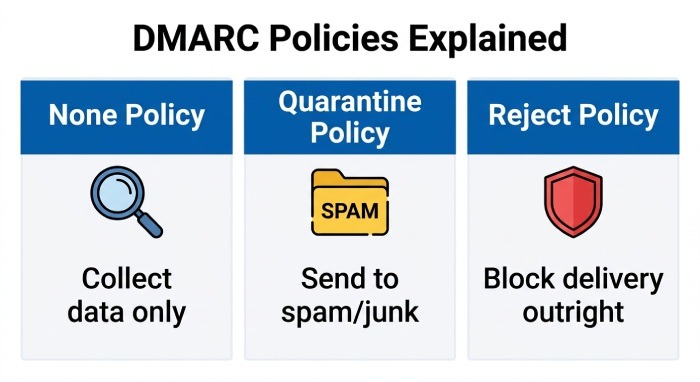
Your DMARC policy is distributed via DNS as a TXT record, generally at _dmarc.example.com. The policy defines how receivers should handle non-authenticating messages:
- none policy: No action—collect data only.
- quarantine policy: Send suspicious emails to spam/junk.
- reject policy: Block outright, rejecting delivery.
DMARC record implementation relies on correct DMARC tags, including pct tag (percentage of messages subjected to policy), rua tag (aggregate report addresses), and ruf tag (forensic report addresses).
DMARC reporting via aggregate report and forensic report provides domain owners with XML feedback (such as afrf and iodef formats) to analyze attempts at unauthorized use.
How to Use an Instant DMARC Checker to Validate Your Record
A DMARC checker streamlines the process of DMARC record testing by performing instant DMARC record lookup, DMARC validation, and misconfiguration detection. Public tools available from entities like MXToolbox, dmarcian, and EasyDMARC allow any domain owner to validate and analyze their DNS record integrity in real time.
Steps in Using a DMARC Record Checker
- Input Your Domain Name: Enter the business or sub-domain (e.g., example.com or _dmarc.example.com) into the DMARC checker interface.
- Initiate DMARC Lookup: The tool retrieves your current TXT record and parses it for all relevant DMARC tags (e.g., v=DMARC1, p, sp, rua, ruf, pct, adkim, aspf, fo, rf, ri).
- Perform DMARC Validation: The DMARC diagnostic tool checks for DMARC syntax errors, validates tag values, and ensures alignment with RFC 7489 specifications.
- Analyze DMARC Implementation and Reporting: The DMARC checker provides detailed validation results, noting proper configuration or calling out issues such as absent rua tag (preventing aggregate report delivery) or incorrect reporting interval (ri tag).
- Review and Apply Fixes: Use the DMARC analysis output to optimize your DMARC policy. Tools like EasyDMARC and dmarcian also help interpret xml feedback and identify areas for enhanced DMARC enforcement and policy distribution.
Understanding the Validation Results
A comprehensive DMARC diagnostic tool will indicate:
- Correct DMARC policy enforcement (none, quarantine, or reject)
- Tag completeness (all required DMARC tags present)
- Alignment parameters (adkim, aspf)
- Reporting setup (rua, ruf, ri, rf)
- Presence of syntax errors or legacy values
- Compatibility with sender requirements
MSPs and large enterprise teams rely on this process to ensure frictionless email program visibility and optimal email deliverability.
Common DMARC Record Errors and How to Fix Them
Publishing a DMARC record without thorough DMARC record testing can lead to critical errors impacting email security. DMARC syntax errors and improper tag configurations are frequent culprits.
DMARC Syntax Errors and Misconfiguration Detection
Typical Problems Include:
- Invalid or unsupported DMARC tags (e.g., a misspelled “p” tag or misused rua/ruf address format)
- Improper alignment values for adkim or aspf tags, causing DKIM alignment or SPF alignment failures
- Omitted required tags, such as missing “v=DMARC1” or policy tag (“p”)
- Incorrect reporting URIs (e.g., missing “mailto:” scheme for rua and ruf tags)
- Invalid reporting interval set by the ri tag
Public tools like MXToolbox and dmarcian are adept at misconfiguration detection and will flag any unsupported or non-standard tags during DMARC analysis.
Fixing DMARC Configuration Issues
- Correct Syntax Errors: Always use RFC 7489 compliant tag values and formats.
- Set Proper Policy and Alignment: Ensure the p tag reflects your enforcement stage and adkim/aspf align with your sender ecosystem.
- Designate Valid Report Receivers: Use verified email addresses in rua and ruf tags.
- Test After Updating: Run DMARC record lookup and validation again after every update.
Domain owners should implement an ongoing DMARC record checker routine to ensure changes reflect instantly.
Best Practices for Monitoring, Updating, and Enforcing DMARC
Achieving and maintaining strong DMARC enforcement is a continuous process that hinges on vigilant monitoring, data-driven policy updates, and periodic record validation.
Proactive DMARC Reporting and Monitoring
- Leverage Aggregate Reports: Use the rua tag to receive regular DMARC reporting in XML format to monitor authentication checks and sender activity.
- Investigate Forensic Reports: Configure the ruf tag for detailed incident reports on DMARC failures to analyze impersonation attempts.
- Automate Analysis: Platforms like EasyDMARC and dmarcian provide dashboard-based analysis—vital for MSPs and enterprises managing multiple domain names.
Updating and Rolling Out Enforcement Policies
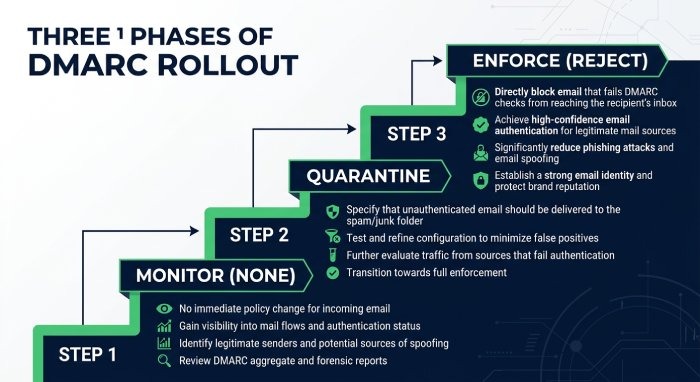
Begin with a None Policy: Start DMARC implementation in “none” mode to collect data without impacting email deliverability.
Gradually Increase Coverage: Use the pct tag to phase in stricter enforcement (quarantine policy, then reject policy) as alignment improves.
Extend Policy to Sub-domains: Utilize the sp tag to ensure sub-domain policy alignment or explicitly set a PARENT_POLICY.
Communication and Training: Keep ESPs, IT teams, and all mail senders informed about new DMARC requirements.
Continuous Validation and Configuration Management
- Schedule Regular DMARC Record Lookup: Run DMARC checker scans after any email security updates, infrastructure changes, or sender policy revision.
- Monitor for DNS Propagation: Ensure every DNS record change (TXT Record for DMARC, SPF, or DKIM) is properly distributed on the Domain Name System.
- Audit for New or Legacy Email Programs: Validate authentication checks for every mail system added or retired.
DMARC diagnostic tools not only help you maintain compliance but also safeguard your organization’s email channel, ensuring robust phishing protection and spoofing protection while optimizing email deliverability for all stakeholders.
Posts You May Like